In this article
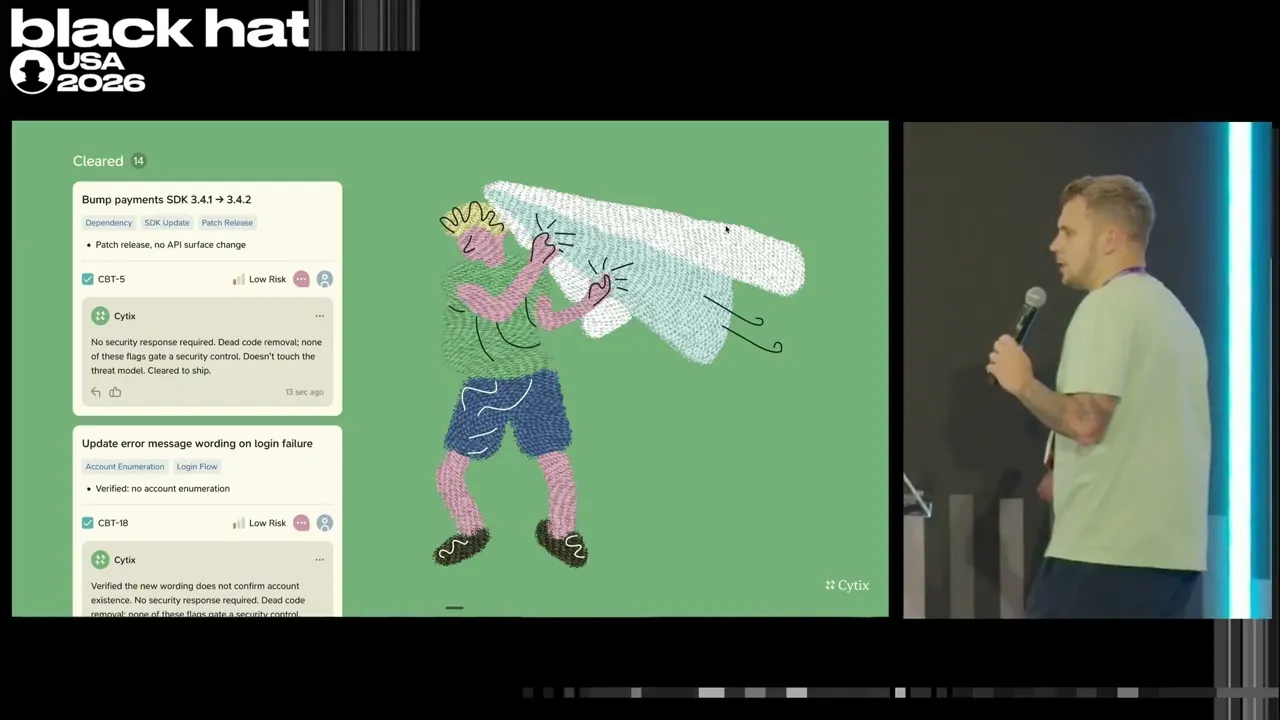
BlackHat USA 2026 Seminar
AI agents have removed the human bottleneck on software change, and security is now the only discipline still governing change on a schedule.
Vulnerability exploitation is the #1 breach vector for the first time in 19 years, time-to-exploit has collapsed from 170 days to under one, and AI-written code introduces semantic flaws (logic and authorisation failures) that scanners were never built to find.
In this session, Ben Armstrong explores the impact of putting a security lens over traditional software change platforms. He explores how security teams move from hoping the right things are validated to knowing they are, and what this means for security.